Can governments decide who gets access to advanced AI models? Are third-party breaches becoming impossible to control? And why are so many CISOs reaching burnout?
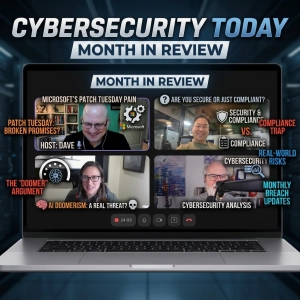
In this special Cybersecurity Today Month in Review Panel, host Jim Love is joined by cybersecurity experts Laura Payne, David Shipley, and Mike Kim (Mycroft) to examine the biggest cybersecurity stories and trends from June 2026.
The panel explores the controversy over U.S. export controls on Anthropic's Mythos and Fable AI models, what they reveal about digital sovereignty, and whether governments should be able to restrict access to frontier AI. They also discuss the continuing wave of third-party breaches, including Salesforce ecosystem compromises and the Clue breach, and why organizations must move beyond compliance toward practical risk management.
The conversation examines FortiBleed, exposed administrator portals, credential reuse, and the difficult balance between software flaws, operational mistakes, and secure-by-default design. The panel also tackles one of cybersecurity's biggest human challenges: CISO burnout, executive accountability, organizational culture, and what separates successful security leaders from those set up to fail.
The episode concludes with encouraging developments in international cybercrime enforcement, including Operation Riptide, and why better intelligence sharing and improved operational security are making it harder for cybercriminals to hide.
Whether you're a CISO, security practitioner, IT leader, or simply interested in the rapidly changing cybersecurity landscape, this discussion offers practical insight into the trends shaping the industry.
Panel
Jim Love (Host)
Laura Payne
David Shipley
Mike Kim (Mycroft)
Topics covered
AI export controls and digital sovereignty
Anthropic Mythos and Fable
Third-party and supply chain risk
Salesforce ecosystem security
FortiBleed and Fortinet security
Secure-by-default strategies
CISO burnout and executive accountability
Operation Riptide
Cybercrime investigations
Security leadership and governance
Chapters
00:00 Sponsor NordLayer
00:38 Meet the Panel
02:40 Author Scam Warning
04:51 Emotion Is the Target
08:47 AI Model Export Controls
10:01 Hype vs Real AI Security
15:01 Sovereignty and Dependency
20:35 Governments Push Back
24:14 AI Internal Voice Risks
26:12 Third Party Breach Fatigue
30:05 Compliance Limits on Risk
32:15 Blame Game to Risk Focus
33:18 Standards and Priorities
33:39 When Security Vendors Fail
34:35 FortiBleed Numbers Explained
35:44 Process Failures vs Bugs
37:32 Why Fortinet Gets Heat
39:05 Secure by Default Basics
41:04 Budget Reality and Culture
44:36 CISO Burnout and AI Pressure
46:16 Liability and Shared Ownership
50:12 What Great CISOs Do
53:07 Operation Riptide Wins
56:10 Deterrence and Due Process
58:14 Sharing Intel for ROI
59:09 Hopium and Wrap Up
01:00:46 Sponsor NordLayer Message