ShieldCrash zero-day breaks Microsoft's newest patch, AI agents compromise 440 school print servers, Fortinet's 92-day streak ends

ShieldCrash zero-day breaks Microsoft's newest patch, AI agents compromise 440 school print servers, Fortinet's 92-day streak ends

Author: David Shipley September 11, 2026 Duration: 10:46

Defender Patch Broken in 24 Hours, AI Agents Hit Papercut Servers, FTC Rolls Back Health App Breach Rules

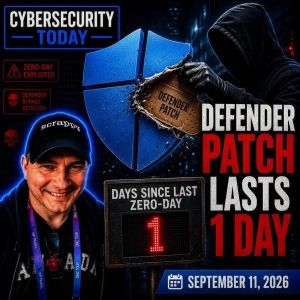
Microsoft patched a Defender zero day, but a day later researcher Nightmare Eclipse released "ShieldCrash," a new exploit that bypasses the ShieldBreak fix, itself a bypass of an earlier Defender flaw, with a proof of concept working on fully patched Windows 10, 11, and Server to enable arbitrary file reads as SYSTEM.

Researchers also tied recent Papercut print server compromises to a suspected Russian-speaking criminal who used hundreds of AI agents (OpenAI Codex and a DeepSeek model) plus tools like Mimikatz and Impacket to rapidly attack 440 servers across 395 organizations in 48 countries, heavily impacting schools and achieving domain admin in 12 cases.

The FTC rescinded a 2021 policy applying breach notification rules to health apps and connected devices.

Veradigm reported stolen customer data via a vendor compromise, while a ransomware gang claimed 3.5 million patient records.

Fortinet went 92 days without a new critical advisory before disclosing two new critical bugs.

Host David Shipley marks the 25th anniversary of 9/11.

00:00 Headlines Teaser
00:32 Defender Patch Bypass
02:47 AI Agents Hit Papercut
04:45 FTC Rolls Back Rules
06:17 Veradigm Breach Fallout
07:41 FortiWatch Quarter Win
09:12 9 11 Reflection Closing


Every morning, Jim Love sifts through the noise of the digital world to bring you a clear, concise briefing on what actually matters. Cybersecurity Today isn't about fearmongering; it's about practical awareness. You'll hear straightforward analysis of the most recent attacks targeting companies, from sophisticated ransomware campaigns to stealthy data theft. Jim breaks down the implications of major breach disclosures, explaining not just what was stolen, but how it happened and who is affected. The focus remains on actionable intelligence-concrete steps and strategic thinking that can help protect your organization's data and infrastructure. This daily podcast serves as an essential filter for IT professionals, business leaders, and anyone responsible for digital assets, transforming complex threats into understandable insights. Tune in for a grounded perspective on navigating an online landscape where the risks are constantly evolving, and the need for clear, timely information has never been greater.
Author: Language: English Episodes: 50

Cybersecurity Today
Podcast Episodes
Inside the North American Water Utility Hacking Crisis [not-audio_url] [/not-audio_url]

Duration: 13:46
Inside the North American Water Utility Hacking Crisis: Iran Links, PLC Tactics, Insurance Fallout, and Volunteer Fixes This special Cybersecurity Today episode examines the expanding wave of water utility intrusions acr…
Wordpress RCE, New Windows 0-day and Coca-Cola's Fairline ransomed [not-audio_url] [/not-audio_url]

Duration: 13:07
New Windows zero-day, Coca-Cola's Fairlife hit by ransomware, and a core WordPress RCE David Shipley covers a new Windows zero-day disclosure from "Nightmare Eclipse" called LegacyHive, a local privilege escalation flaw…