Ship It Conversations: Guardsquare’s Joel DeStefano on Mobile App Security, Runtime Protection, App Hardening, and Why Scanning Isn’t Enough

Ship It Conversations: Guardsquare’s Joel DeStefano on Mobile App Security, Runtime Protection, App Hardening, and Why Scanning Isn’t Enough

Author: Teller's Tech - DevOps, SRE and Cloud Podcast June 21, 2026 Duration: 35:58

This is a guest conversation episode of Ship It Weekly, separate from the weekly news recaps.

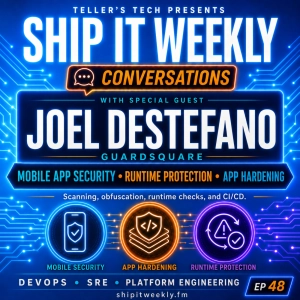
In this Ship It: Conversations episode, I talk with Joel DeStefano from Guardsquare about mobile app security, why it is different from backend and cloud security, and why scanning alone is not enough once an app is shipped into the real world.

We talk about the shift in trust model that happens with mobile apps. In backend and cloud systems, teams usually have more control over the runtime, infrastructure, policies, and monitoring. With mobile, the app becomes a public artifact running on someone else’s device, in an environment you do not fully control.

The bigger theme here is that mobile security is not just “scan it before release.” Scanning matters, but teams also need to think about app hardening, obfuscation, runtime protection, monitoring, and whether the app connecting back to their APIs is genuine and uncompromised.

Highlights

• Why mobile changes the trust model compared to backend and cloud systems

• What DevOps, SRE, and platform teams should understand about mobile app risk

• Why scanning is useful, but not enough by itself

• The danger of assuming app store approval means an app is secure

• Why “we do not store sensitive data in the app” can be a misleading security argument

• How attackers can reverse engineer apps, inspect workflows, and learn how the app talks to backend APIs

• What code hardening and obfuscation actually help protect against

• Why runtime checks matter for rooted devices, compromised environments, debuggers, hooking frameworks, overlays, and accessibility abuse

• The difference between Android and iOS security assumptions

• Why the OS is not responsible for protecting your app’s business logic

• How mobile security should fit into CI/CD without destroying release velocity

• What should block a release versus what should become tracked risk

• Why testing, hardening, runtime protection, and monitoring should work together as one strategy

• How AI may speed up attackers without fundamentally changing the need for strong security fundamentals

• Joel’s advice for improving mobile security posture: start with the app’s critical workflows, backend interactions, and real business risk

Joel / Guardsquare links

• Guardsquare: https://hubs.ly/Q04fJgkJ0

• Guardsquare Blog: https://www.guardsquare.com/blog

OWASP mobile security links

• OWASP Mobile Application Security: https://owasp.org/www-project-mobile-app-security/

• OWASP MASVS: https://mas.owasp.org/MASVS/

Our links

More episodes + show notes + links: https://shipitweekly.fm

On Call Brief: https://oncallbrief.com


For anyone building or running modern systems, the sheer volume of news, tools, and incident reports can be overwhelming. Ship It Weekly cuts through that noise. This isn't a surface-level scan of headlines. Host Brian Teller digs into the latest significant outages, major software releases, and insightful post-mortems, focusing squarely on the practical implications for DevOps, SRE, and platform engineering work. Each episode of the podcast breaks down a couple of key stories, providing the crucial context often missing from tech news. You'll hear analysis that translates events into actionable insights, answering the "so what?" for your own infrastructure and processes. The show also includes a quick rundown of tools or updates actually worth your attention, saving you hours of browsing. The tone is direct and informed, favoring depth over breadth. It’s designed for engineers and technical leaders who need a concise, reliable filter for the week's most relevant developments. Listen to this podcast for a focused recap that prioritizes what actually matters, delivered without fluff. You get the news, plus the necessary interpretation to understand how it might affect your systems, your team, and your on-call rotation. It's a weekly briefing that respects your time while aiming to make you more effective.
Author: Language: English Episodes: 50

Ship It Weekly - DevOps, SRE, Platform and Cloud Engineering News
Podcast Episodes
GitHub Outage, PleaseFix Agentic Browser Vulnerability, AWS Certificate Manager Drops Email Validation, Cloudflare TypeScript CI Workflows, AI Observability Consolidation, and the Hidden Cost of “Simple” Platform Changes [not-audio_url] [/not-audio_url]

Duration: 17:39
This week on Ship It Weekly: GitHub suffers another widespread outage affecting the web interface, APIs, Actions, authentication, Copilot, and other critical developer workflows. Zenity Labs demonstrates PleaseFix attack…